Temporary email is useful when you need an address for a short-lived interaction but do not want to expose your primary mailbox. The important distinction is that a temporary inbox is a privacy boundary, not a place to store valuable identity, financial, or recovery information. Used deliberately, it reduces marketing exposure and keeps testing traffic separate from personal mail.
What temporary email actually protects
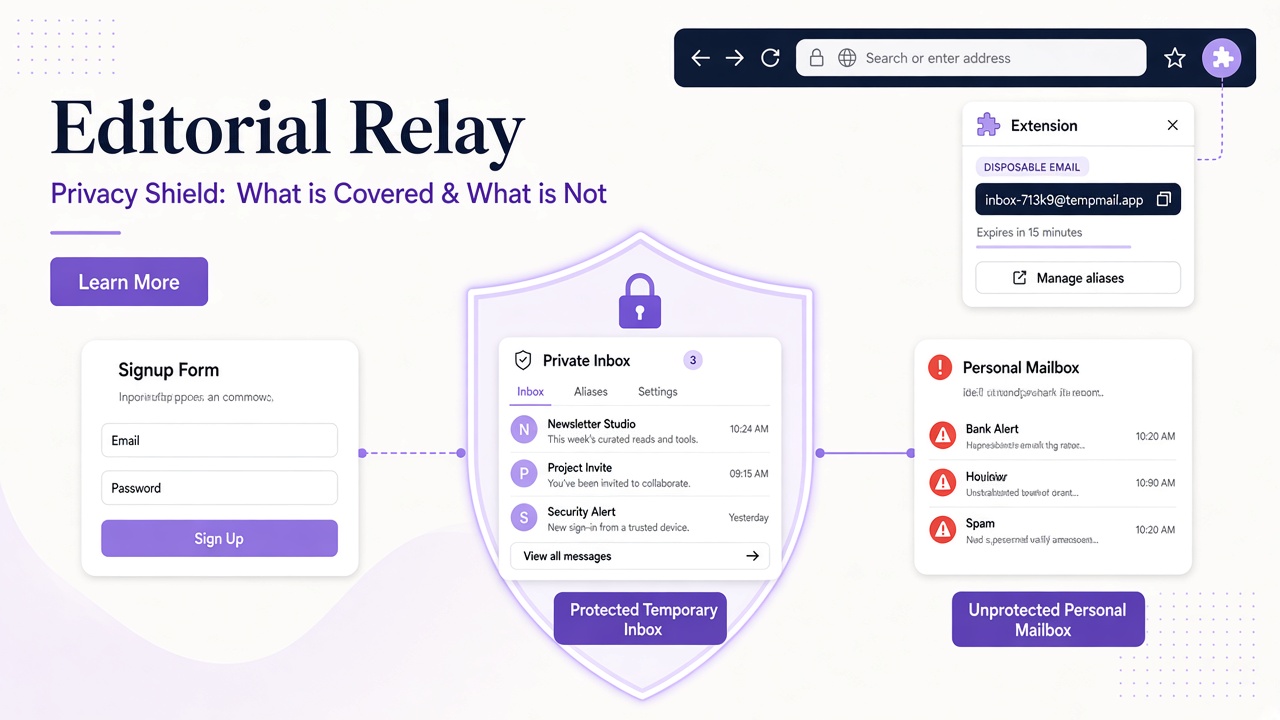
A temporary address can reduce the number of services that know your primary address. It can also isolate verification messages, trial accounts, QA traffic, and newsletter experiments. It does not make you anonymous, encrypt a message, or guarantee that a sender cannot identify you through other signals.
| Use case | Good fit | Better alternative when stakes are high |
|---|---|---|
| One-time download | Temporary inbox | A secondary mailbox for long-term access |
| Product trial | Temporary inbox | Alias with recovery access |
| Email verification testing | Relay test inbox | Staging mail service for regulated data |
| Password recovery | Avoid temporary inbox | A durable, protected mailbox |
A safer signup workflow
Create the address before submitting a form, save the access method only for the duration of the task, and verify that the incoming message belongs to the service you intended to use. Read the message as untrusted content. Do not follow a link merely because it appears in an email; compare its domain with the product you are testing. Relay can expose OTP candidates and authentication links, but your application still owns the final decision.
For developers, the Relay inbox guide explains access passwords and the REST API provides scoped automation. If you are building an agent workflow, use the MCP integration and keep message content below the instruction boundary.
Retention and access review
A privacy workflow should have an end. Record the inbox identifier rather than the full message body, remove local test artifacts according to your project policy, and revoke credentials that are no longer needed. Never place OTPs, access passwords, or full email bodies into public CI logs.
Frequently asked questions
Is temporary email anonymous?
No. It limits primary-address exposure but does not remove network, browser, payment, or account signals.
Can I use it for account recovery?
Use a durable mailbox you control for recovery and important notifications.
How should developers automate it?
Use a dedicated inbox per test worker, a deadline-based polling loop, and the TypeScript SDK guide.
A signup desk scene
You are evaluating three SaaS trials for a legitimate purchase decision. Each vendor sends onboarding mail, security alerts, and marketing drips. Routing all three through your work address mixes procurement evidence with newsletters you may never unsubscribe from. Three separate Relay inboxes—one per evaluation—keep receipts findable without touching your primary mailbox.
| Signal you are protecting | Temporary inbox helps? | Limit |
|---|---|---|
| Marketing volume | Often | Does not block browser fingerprinting |
| Wrong-thread replies | Yes | You must still save guest passwords |
| QA noise | Yes | Not a substitute for data-classification policy |
Pair this with the broader temporary email privacy collection when you need a longer-form threat-model discussion.